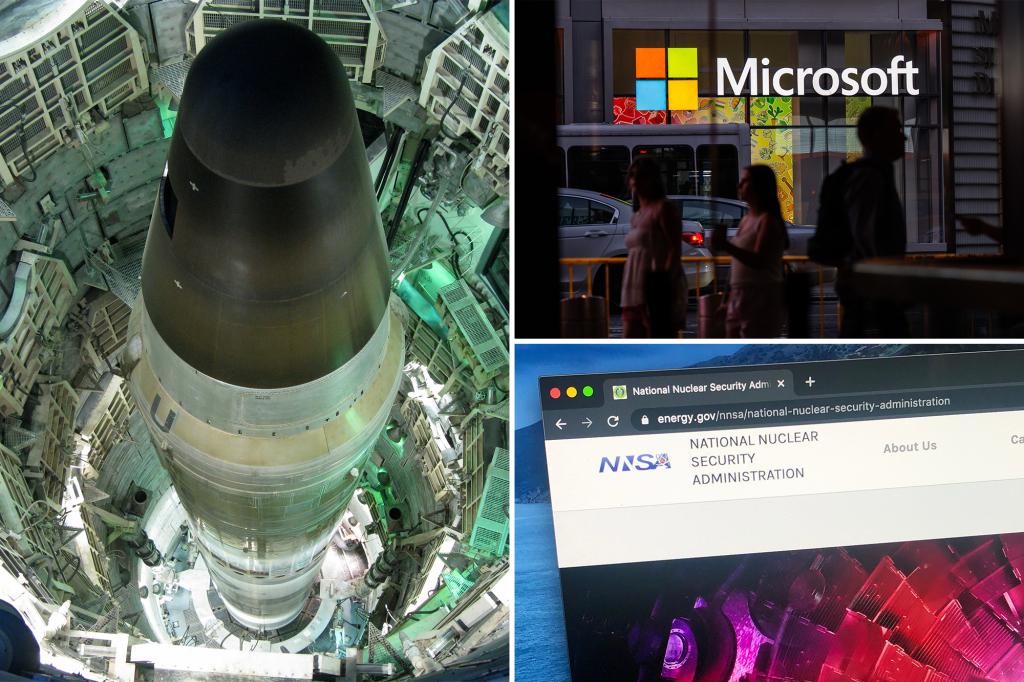

Microsoft has issued a warning that hackers sponsored by the Chinese state have infiltrated its SharePoint software, which is utilized by the US agency that handles the upkeep and advancement of the country’s nuclear weapons arsenal, as stated in a report.
The National Nuclear Security Administration, which operates with some autonomy under the Department of Energy, was reportedly one of the entities attacked by Chinese-backed cybercriminals, Bloomberg News reported.
A Dutch cybersecurity firm estimates that about 400 government entities in the United States, Mauritius, Jordan, South Africa, and the Netherlands have been affected by the breach, according to Bloomberg News.
The Dutch firm, Eye Security, previously estimated that just 60 entities were impacted.
A source familiar with the situation told the financial news site on Tuesday that no sensitive or classified information was known to have been stolen in the hack, which was made possible by exploiting a flaw in Microsoft’s SharePoint document management software.
“On Friday, July 18th, the exploitation of a Microsoft SharePoint zero-day vulnerability began affecting the Department of Energy,” an agency spokesman told Bloomberg News.
“The department was minimally impacted due to its widespread use of the Microsoft M365 cloud and very capable cybersecurity systems. A very small number of systems were impacted. All impacted systems are being restored.”
The breaches have been ongoing since at least July 7, according to Adam Meyers, senior vice president at CrowdStrike, the cybersecurity firm that has partnered with Microsoft to ward off potential cyber threats.
“The early exploitation resembled government-sponsored activity, and then spread more widely to include hacking that ‘looks like China’,” Meyers told Bloomberg News. CrowdStrike’s investigation into the campaign remains ongoing.
The Post has sought comment from the NNSA, Microsoft, CrowdStrike and Eye Security.
In a blog post, the tech giant identified two reputed cybercriminal organizations, Linen Typhoon and Violet Typhoon, in the alleged scheme to exploit flaws in Microsoft’s software that is used by customers on their own networks rather than in the more secure cloud.
These customers are at risk of having their data compromised by the hackers, according to Microsoft, which also fingered a third Chinese-based organization, Storm-2603, as doing the same.
Every morning, the NY POSTcast offers a deep dive into the headlines with the Post’s signature mix of politics, business, pop culture, true crime and everything in between. Subscribe here!
Microsoft SharePoint is a platform used to store, organize, share and manage internal web content across an organization — similar to intranets.
The NNSA wasn’t the only agency that was targeted in the alleged cyberattack.
Among the victims are the US Department of Education, Florida’s Department of Revenue and the Rhode Island General Assembly, which is the Ocean State’s legislative body.
Internationally, governments in Europe and the Middle East have also been targeted. Cybersecurity researchers have detected breaches on more than 100 servers, representing at least 60 victims across various sectors, including energy, consulting and academia.
Microsoft has patched the vulnerabilities in recent days, but the company expressed concern that hackers will continue to exploit these flaws in future attacks.
“We have high confidence that threat actors will continue to integrate them into their attacks,” Microsoft stated in its blog post.
“China opposes and fights hacking activities in accordance with the law. At the same time, we oppose smears and attacks against China under the excuse of cybersecurity issues,” a spokesperson for the Chinese embassy said in a statement.
Cybersecurity experts have expressed grave concerns about the severity of the threat.
Michael Sikorski, chief technology officer and head of threat intelligence for Unit 42 at Palo Alto Networks Inc., described the situation as a “high-severity, high-urgency threat.”
He emphasized the risks posed by SharePoint’s deep integration with Microsoft’s ecosystem, which includes services like Office, Teams, OneDrive and Outlook — all of which contain valuable data for attackers.
Eye Security reported that the flaws allow hackers to access SharePoint servers and steal authentication keys, enabling them to impersonate users or services even after patches are applied.
“We estimate that the real number might be much higher as there can be many more hidden ways to compromise servers that do not leave traces,” Eye Security’s co-owner Vaisha Bernard said in an email to Bloomberg News.
“This is still developing, and other opportunistic adversaries continue to exploit vulnerable servers.”
Despite Microsoft’s efforts to bolster its security measures, including hiring executives from government agencies and holding weekly security meetings, the recent breaches have drawn renewed scrutiny.
The US government issued a report last year that was critical of Microsoft’s lax security culture.