Hackers linked to Iran have set their sights on American companies in a recent cyber offensive, stirring apprehensions that critical infrastructure could soon be at risk. This alarming development underscores the ever-present threat of cyber warfare in today’s digital landscape.
On Thursday, cybersecurity specialists revealed that the Advanced Persistent Threat (APT) group known as Seedworm has successfully breached several organizations. Among the targets are a financial institution, an airport, and a defense and aerospace industry software supplier, highlighting the diverse range of their attacks.
Investigations conducted by experts from Symantec and Carbon Black found that the attackers had deployed a concealed malicious program, commonly referred to as a backdoor. This tool enables the hackers to regain access to the compromised systems undetected, posing a significant threat to the integrity of these networks.
While the names of the affected companies remain undisclosed, the implications of such breaches are profound. The cybercriminals appear to be engaged in espionage, exfiltrating sensitive data and possibly laying the groundwork for future operations.
Researchers caution that these cyber intrusions are more about sending a political message than merely pilfering information. They stressed that any organization within the targeted nation could potentially be at risk, emphasizing the broad scope of the threat.
‘These attacks are about sending a message rather than stealing information, which means any organization in the targeted country could be in the firing line,’ the researchers warned.
The cyber activity comes as the US and Israel launched a major military offensive against Iran that killed the country’s supreme leader and several senior officials.
‘Because of the heated tension in the region and ongoing attacks, it is likely Iran and its allies may also initiate cyber operations to further target their adversaries,’ the researchers said.
The cyber activity comes as the US and Israel launched a major military offensive against Iran, killing the country’s supreme leader and several senior officials.

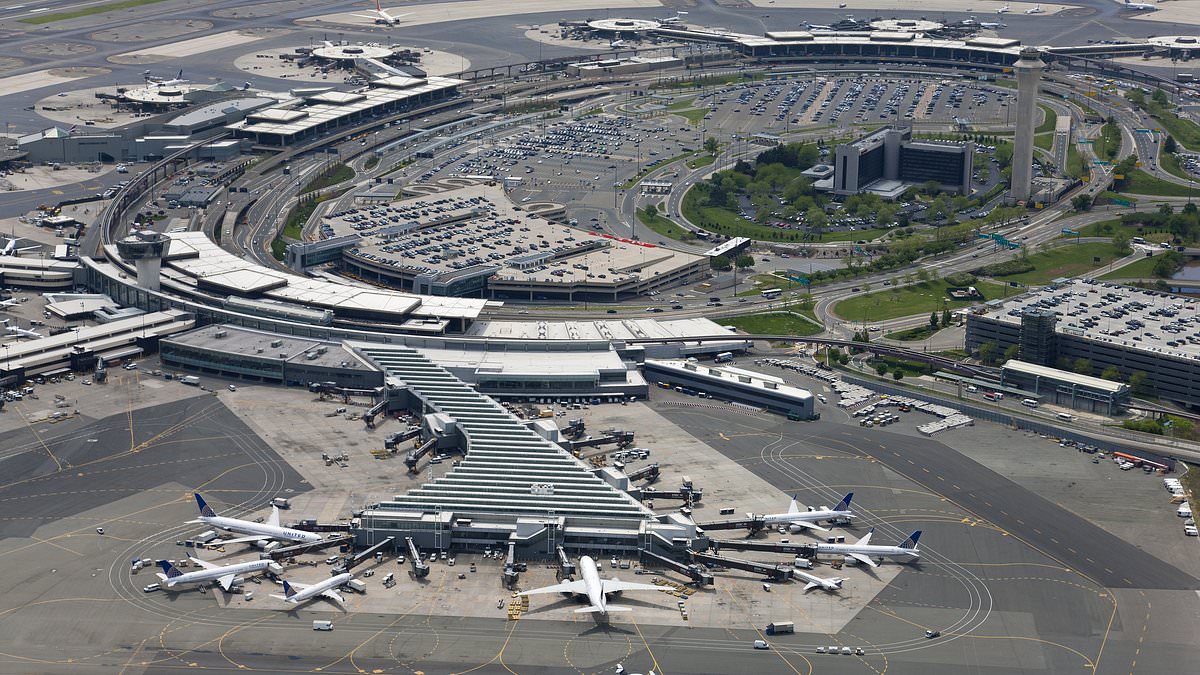
Cybersecurity experts revealed Thursday that the Iranian hackers had infiltrated multiple US organizations, including a bank, an airport and a software supplier to the defense and aerospace industries (STOCK)
Iran has previously demonstrated significant cyber capabilities, particularly during periods of heightened geopolitical tension.
The cybersecurity experts warned that any future attacks could target critical sectors such as energy and utilities, transportation and logistics, finance, telecommunications, healthcare, and companies linked to defense and military supply chains.
The hacking group, also known as MuddyWater, Temp Zagros and Static Kitten, is believed to be part of the Iranian Ministry of Intelligence and Security (MOIS).
The activity appears to have begun in early February and has continued in recent days, even after US and Israeli military strikes on Iran, the cybersecurity researchers shared in a blog.
Several organizations have reported suspicious activity on their systems in recent weeks, including a US bank, an airport and a software company that supplies technology to the defense and aerospace industries.
Non-profit organizations in both the US and Canada were also affected.
Researchers said the software company operates in Israel, and its Israeli branch appears to have been the primary target of the activity.
They also discovered a previously unknown piece of malware, a hidden access tool they named ‘Dindoor,’ on the systems of the company’s Israeli branch.

Investigators said the hackers appeared to be spying, stealing sensitive data and positioning themselves for potential future attacks
The same backdoor was later found on the networks of a US bank and a Canadian non-profit organization, suggesting the attacks were part of a broader campaign.
The malware uses a programming tool known as Deno to run commands on infected systems and was digitally signed with a certificate issued to the name ‘Amy Cherne.’
Investigators also detected an attempt to copy data from the software company’s systems to external cloud storage using a file-transfer tool called Rclone.
However, it remains unclear whether any information was successfully stolen.
The experts warned that Iranian cyber groups may escalate their operations, potentially combining disruptive attacks with quieter efforts to gain access to sensitive systems.
‘The likely next steps for the nation’s cyber actors and supporters may be multiple campaigns combining high-visibility disruption for political signaling and lower-visibility access operations for strategic leverage,’ the researchers said.
The attacks come as cybersecurity firm CloudSek released a threat landscape assessment warning that more than 60 hacker groups mobilised within hours of the February 28, 2026, US-Iran military escalation.
They added that tens of thousands of US industrial control systems remain directly reachable from the internet, many with no authentication beyond a factory-default password.


