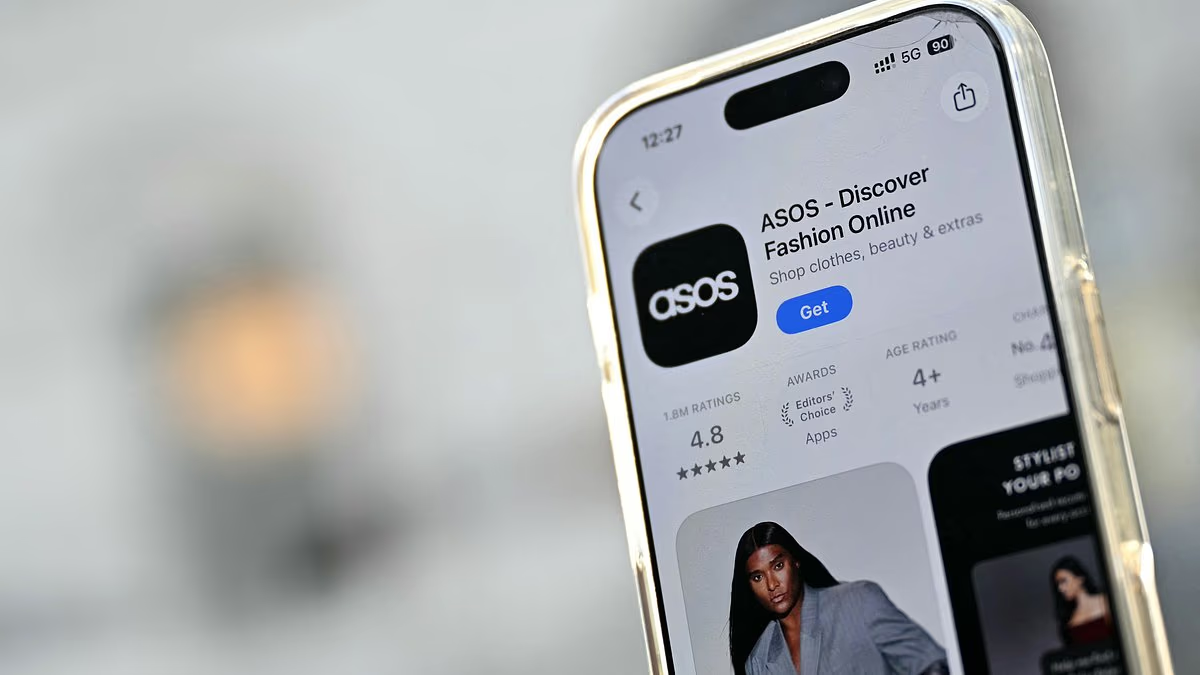

Online fashion retailer Asos was apparently targeted by hackers yesterday after customers received messages on their phones threatening to expose personal information.
Asos acknowledged that some “basic personal information” may have been accessed, following what cyber-security specialists described as an unusually bold communication directed at the company’s customers.
The alert appeared through the Asos app yesterday morning under the heading “ASOS hacked”. It claimed: “Dear ASOS DPO and IT, we have full compromised the Snowflake instance. Engage with us, or we will leak it: t.me/xuanyewengateway.”
The reference to a DPO relates to the data protection officer responsible for overseeing the security of personal information. Snowflake is a cloud-based service used by businesses to store, manage and analyse data.
More than five hours after the unauthorised alert was sent, Asos said that basic customer details might have been accessed. However, the company said it had no reason to believe payment-card data or account passwords had been affected.
The retailer also said its own platform had not been compromised.
Reports later claimed that the alleged attackers had given Asos two weeks to pay a ransom, warning that customer information could otherwise be released.
The push notification directed recipients to a Telegram channel linked to a group calling itself the Xuanye Group. The channel had reportedly been created on the same day as the alert.
Messages subsequently posted there allegedly claimed that customer data was being held securely on the group’s server and would not be interfered with for a set period.
One message attributed to the hackers reportedly said: “Considering the current situation regarding incident disclosure in the cyber-security landscape, you can thank us for our generous clarity regarding this incident.”

Asos appears to have been targeted in a cyber incident after customers received threats that their data could be leaked

Asos says it serves 17 million customers across 150 countries, while its website and app appeared to remain operational despite the suspected breach
The Telegraph reported that the attackers had sought a ransom from Asos in return for deleting the customer information they claimed to possess.
A message shared on Telegram reportedly stated: “Our message is clear and simple to recognise. The organisation must contact us or we will leak it [customers’ data]. That is what we said. The two-week period is intended for them to make contact; they know what happened.”
Cyber-security experts said the striking customer notification appeared intended to create alarm and pressure the retailer into responding quickly.
Asos apologised to customers who received the unauthorised push notification in a statement issued yesterday afternoon.
“Asos can confirm that, at around 10am today, an unauthorised customer notification was sent to Asos customers,” the company said in a further announcement to the London Stock Exchange.
“We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers. We took immediate action to restrict access to the notification platforms and are working with our internal and external specialist advisers, as well as all relevant authorities.”
“Basic personal information, including names and contact details, may have been accessed. We do not believe that payment-card information or account passwords were affected.”
“Our website and app are operating normally, with no current disruption to any part of our operations. Customer trust is incredibly important to us, and we will provide an update if the situation changes.”
‘The Company has cyber security insurance with a large global provider, including business continuity insurance. It is too early to quantify any potential impact on trading.’
Katherine James, director of Snowflake’s Europe, Middle East, and Africa communications team, told the BBC: ‘As soon as we became aware of the notification that is currently being reported, we began an investigation.
‘At this time, we can report that we have found no compromise of the Snowflake platform. We take customer privacy and security very seriously.
‘The investigation is ongoing and we will provide further updates as soon as more information becomes available.’
Asos, which also owns brands including Topshop and Miss Selfridge, says it has 17 million customers in 150 countries. Its website and app appear to be working still despite the apparent breach.
The firm’s shares fell by 11 per cent after reports of the hacking emerged.
Panicked customers reacted online to the ‘crazy notification’, and some said they had ‘never deleted my payment methods so quick’.
Marie Wilcox, VP of market strategy at cyber-security firm Binalyze, said: ‘This notification was psychological warfare, designed to whip up panic. Attackers know that any panic piles on the pressure on Asos to think about paying up rather than taking time to develop a rational response.’
The National Cyber Security Centre, which is part of Britain’s intelligence agency GCHQ, has offered Asos assistance, reported the BBC.
Aimee Speight, communications expert and founder of crisis PR agency Highland Consulting, said the hackers had done a better job at communicating than Asos.
She said: ‘Customers heard about this breach from the people behind it, in ASOS’s voice, through ASOS’s own app. Every hour of silence lets that story harden. ASOS doesn’t need every answer to speak: “we’re aware, we’re investigating, here’s when we’ll update you” starts to take the narrative back.
‘They should be telling customers clearly what not to do: don’t tap the notification, don’t join the Telegram channel, and ASOS will never ask for your password by link. The phishing wave that follows a story like this is often more damaging than the original breach.
FIND OUT MORE: America’s ‘Scariest Road’ Keeps Killing, Yet No One Will Fix It
‘The real risk now is the convincing “ASOS refund” email or “account problem” text that arrives next week.
‘”Don’t click this link” covers this morning’s notification. It does nothing for the next one. Customers needed a clear line: ASOS will never ask for your password or card details by email, text or link. That line is missing.’
Asos is legally obligated to tell customers if their data has been breached under the UK’s data protection law.
Kat Cereda, from Which?, told the BBC this should be done ‘without any undue delay’ and the firm should ‘explain the consequences and outline what steps they are going to be taking to protect you’.
Marijus Briedis, chief technology officer at NordVPN, said it was ‘an unusually brazen and threatening message’.
He said: ‘The attackers aren’t simply claiming to have breached Asos – they’re publicly telling the company to engage with them or they will leak what they say they have obtained.’
Mr Briedis said if the claims made by the hackers are genuine, ‘the critical question will be what information was held there and whether any of it was accessed or downloaded’.
‘At this stage, however, customers shouldn’t assume their personal or payment information has been stolen – that hasn’t been established,’ he said.
‘What customers should be particularly alert to now is what happens next. High-profile cyber incidents create ideal conditions for phishing attacks.
‘Criminals may exploit the publicity by sending emails and texts claiming to be from ASOS, perhaps asking customers to reset a password, confirm payment details, check an order or claim a refund.’

Asos released a statement on its social media channels more than five hours after the notfication was first sent
He added: ‘But this incident shows how powerful access to a trusted communications channel can be. When an attacker can potentially speak to customers through a company’s own systems, it makes the threat considerably more convincing and potentially much more damaging.’
Dr Pete Membrey, the chief research officer at ExpressVPN, said the worst thing people can do is panic.
‘Getting a message like that from an app you trust is genuinely unsettling,’ he said.
‘Most people think of a hack as something that happens out of sight, so seeing a threat land on your own phone makes it feel much more personal.’
Dr Membrey advised Asos customers to do ‘some simple due diligence. Don’t tap on the notification or follow the link in it. Go to the Asos website directly, by typing in the address yourself rather than through an email or the app, and reset your password.’
Kamran Bahdur, chief information officer at cyber-security firm FLR Spectron, advised Asos customers to change their passwords ‘for an extra layer of protection and peace of mind’.
He said: ‘This should be taken seriously and treated as a potential extortion attempt until we’ve verified the facts.’
Cyber security expert Jake Moore described it as ‘one of the most visible hacks in history’ and could ‘put a lot of customer data at risk’.
‘By broadcasting their breach directly to Asos app users, the threat actors are likely trying to apply pressure to Asos, showing how extensive their access is so they can leverage some sort of ransom,’ the global cyber security adviser at ESET told the Independent.
He said the fact hackers had sent the message through Asos’s app suggests they had gained access to some of the firm’s systems.
But Mr Moore said it doesn’t ‘prove their full claims about the extent of the data breach’.
Charlotte Wilson, head of enterprise at cyber-security firm Check Point, told the BBC: ‘If confirmed, this is a deeply serious attack because the hackers appear to have done something particularly brazen: turned ASOS’s own app into their ransom note.’
Britain is Asos’s largest market, representing 49 per cent of all revenues in the first half of the latest financial year.
The fast-fashion firm is undergoing a major turnaround programme to halt declining sales and return to profit.
Mike Ashley’s Frasers Group owns 29.26 per cent of Asos and is the firm’s largest shareholder.
Britain has been hit by several cyber attacks in recent months. In August, up to 1,000 charities, including Breast Cancer UK, English National Ballet and the Molly Rose Foundation, were targeted.
Criminals targeted Beacon CRM, which provides customer management software to the charity sector.
It is thought the firm mistakenly published an access key online that allowed hackers to copy its databases.
Meanwhile, M&S and Co-op were left crippled by a cyber-attack in the spring and summer of 2025.
Notorious hacker group Scattered Spider was linked to the attack that left shelves empty for weeks and forced M&S to stop accepting all online orders and payments.
Have YOU been affected? Email matt.strudwick@dailymail.co.uk